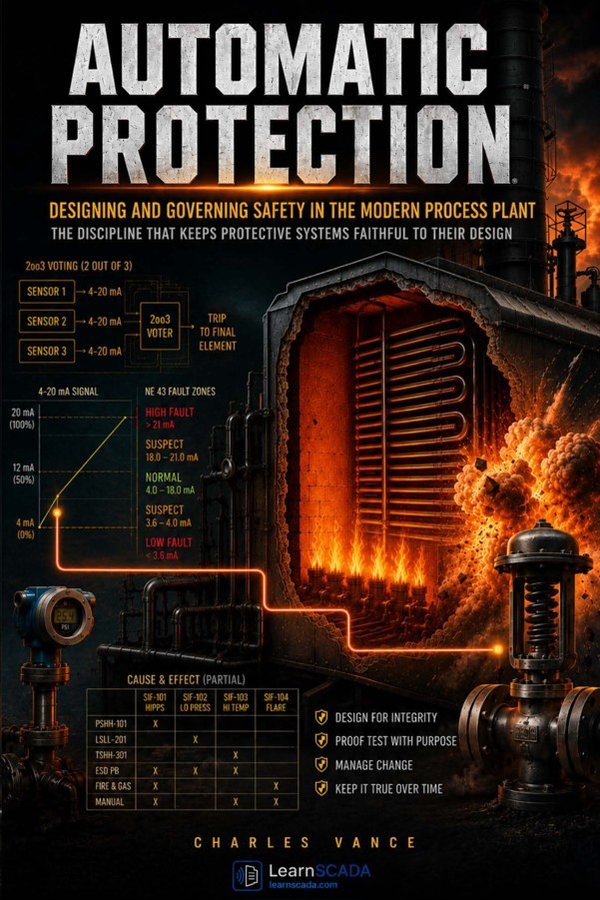
Automatic Protection
Designing and Governing Safety in the Modern Process Plant
A unit keeps tripping on a transmitter that has gone bad, and someone asks the obvious question: why not just disable the trip? Automatic Protection is the answer to that question, and to the hundred others like it that quietly decide whether a protective system actually protects.
Written for the engineers who build and maintain protective systems in Ignition and Rockwell, this is a working field guide to getting automatic protection right. It starts from first principles: what bad quality really means, why fail-safe is a design choice, and how a cause-and-effect matrix becomes the law of the plant. It then moves through voting architectures, SIL, and LOPA, and into the controller logic, the HMI annunciation, and the forensic record that proves what happened after a trip. It closes with the operations discipline that keeps protection sound for decades: bypasses and overrides, alarm floods, proof testing, and management of change.
One argument runs through every chapter: the conflict between safety and availability is almost always an artifact of a single transmitter, and the fix is architecture, not amputation. When a trip is costly, you buy back availability with redundancy and good design; you do not quietly remove a layer of protection and hope. Plainspoken, standards-aware (ISA 18.2, IEC 61511, NAMUR), and built on real plant experience, it is the book to hand the new engineer, and the one to keep beside the keyboard when the pressure is on to take a shortcut.
- Author
- Charles Vance
- Category
- How a Plant Works
- Paperback ISBN
- 9798182098731